

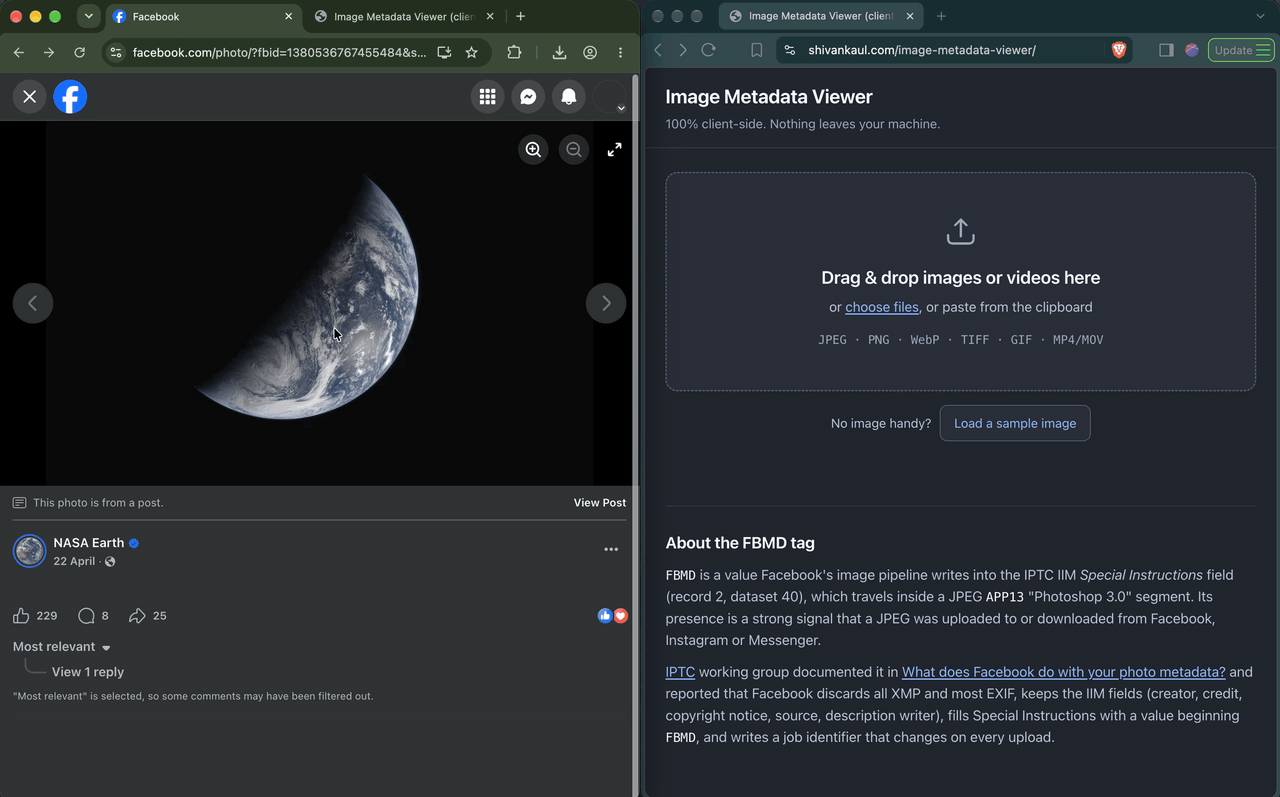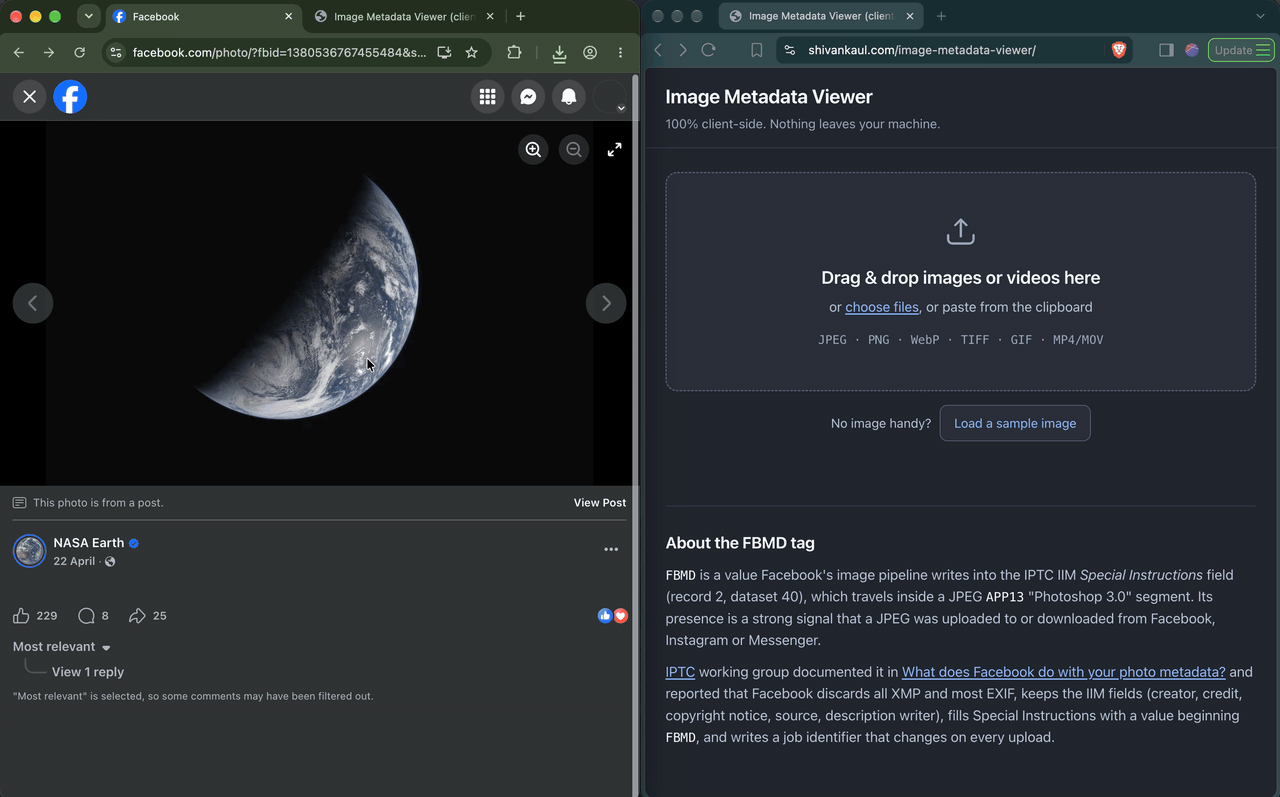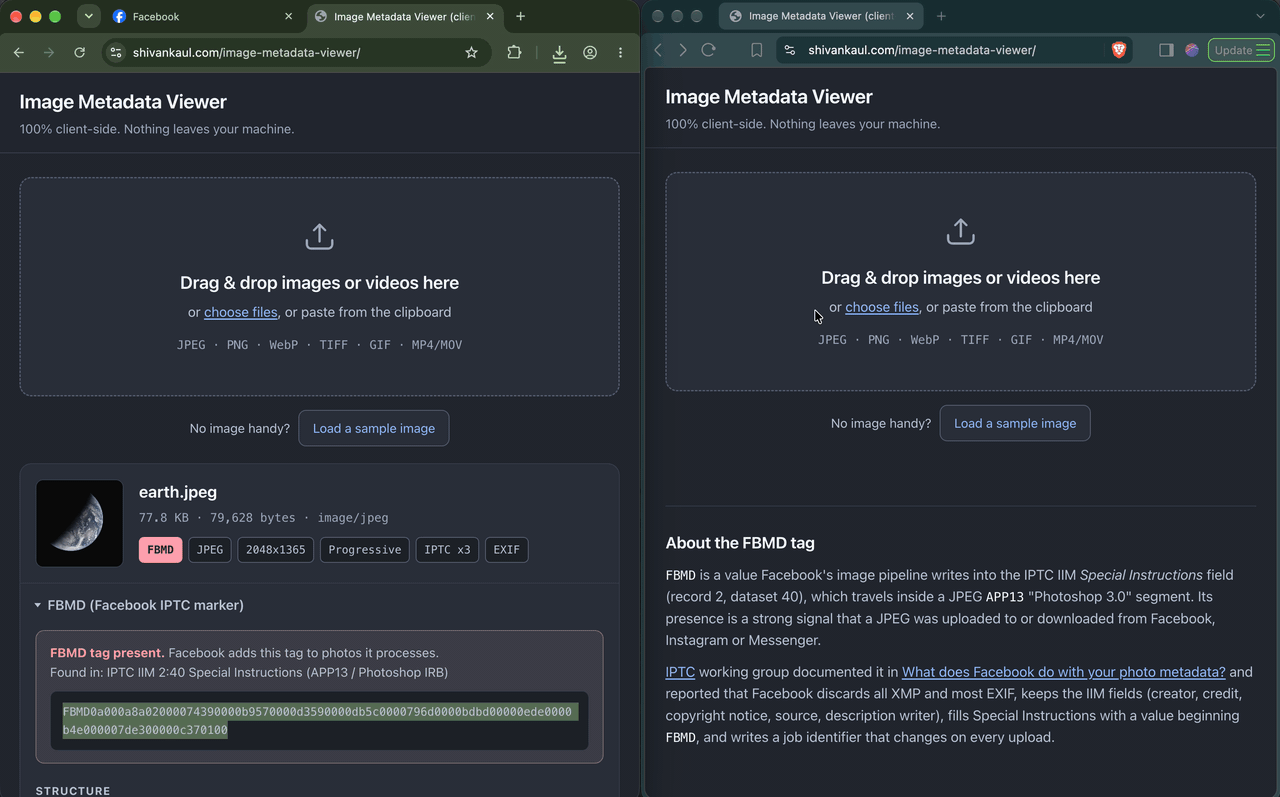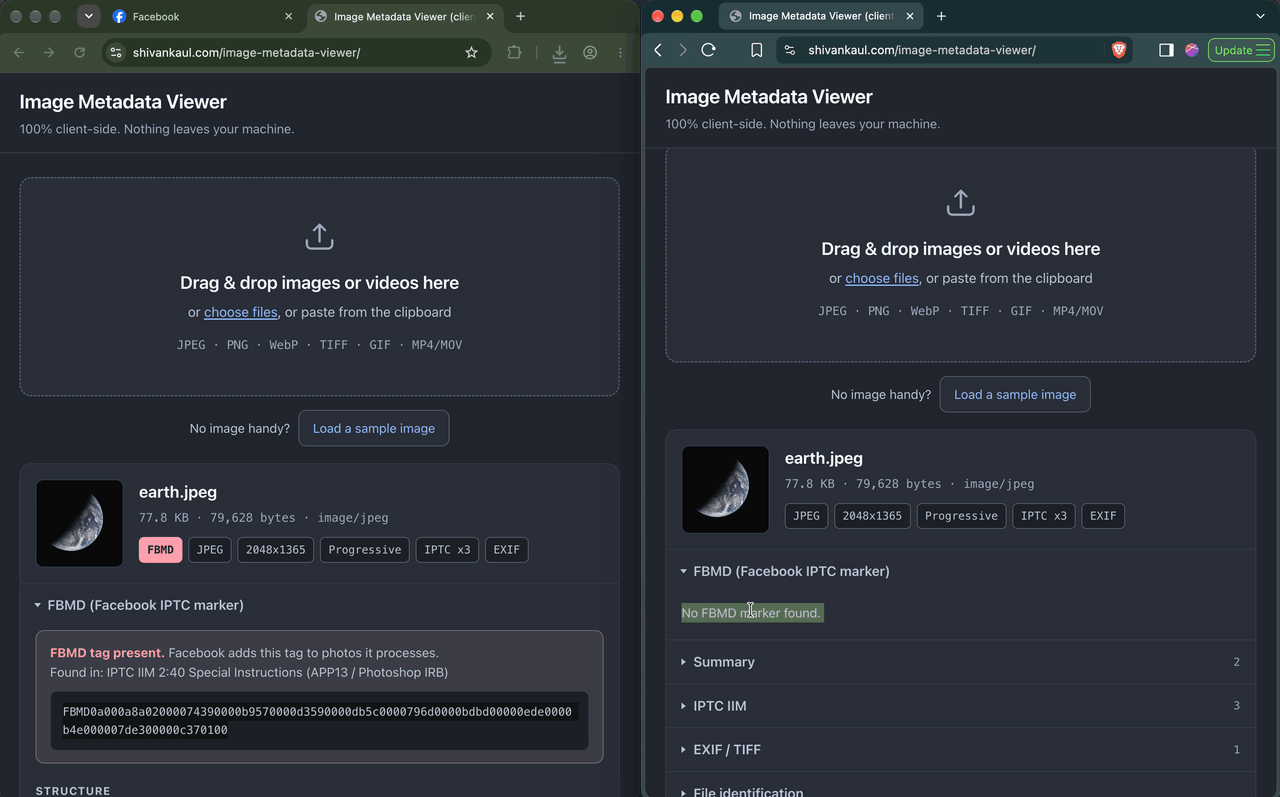
How Brave removes the identifier Brave removes the FBMD identifier at two points:
When you save an image, Brave removes the identifier before the download finishes. This protects you even if you upload the image later with another browser or app. When you upload an image to a website, Brave uploads a clean copy. The original file on your computer stays as it is. Brave’s metadata stripper is written in C++ with no extra libraries, so it stays small and fast. You can follow the work on GitHub.
IDGAF what brave does, neither the company nor their browser should be trusted. They’ve done a lot of sketchy and hateful shit:
@[email protected] is the author of everything that follows:
This is a very well written an thorough article and I highly recommend reading it. If you don’t want to however, here is a summary of the key points:
Brendan Eich’s anti-LGBTQ+ political involvement
2016 — Brave Browser promises to replace webpage ads
2018 — Brave runs a questionable donation campaign
2020 — Brave injects referral links when visiting crypto wallets
2020 — Brave puts ads in user’s home screens
2021 - Brave ships an insecure Tor feature
2023 - Brave hides their crawlers to websites
2024 - So-called “privacy browser” deprecated advanced fingerprinting protection
And More!
So what exactly is the problem with them hiding their crawler from websites? I read the accompanying article but I don’t really see the issue?
It’s like banning someone from your store, only for them to come back in a disguise. It’s effectively digital trespassing and a violation of your consent.